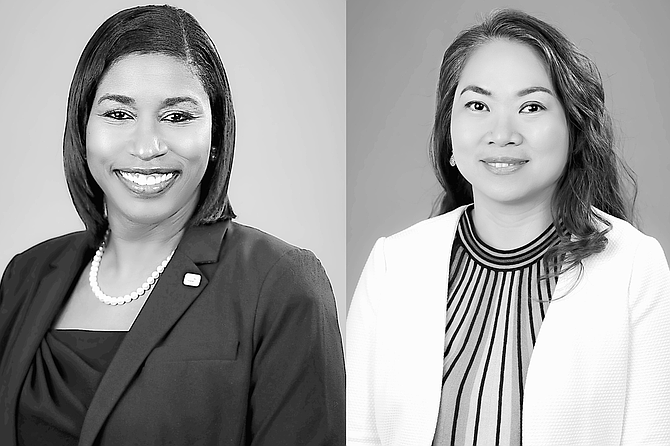
(L) Myra Lundy-Mortimer and (R) Nestle Maullon
The rise of artificial intelligence (AI) threats is making cyber security increasingly more a complex, a Bahamian accountant is warning, adding that it must be viewed more broadly than simple technology risks.
Myra Lundy-Mortimer, territory assurance leader and risk assurance partner for PricewaterhouseCoopers (PwC) Bahamas, spoke out as a global survey by the accounting firm found 84 percent of corporate respondents expect cyber security budgets to expand to meet potential AI threats and challenges.
She said: "The emergence of AI-driven threats is creating a new level of complexity for organisations, particularly at a time when many are still strengthening their broader cyber resilience capabilities.
“As the threat landscape evolves, leaders must move beyond viewing cyber security solely through a technology lens and ensure cyber risk is considered as part of enterprise-wide decision-making.
“Building resilience requires strong governance, clear accountability and an understanding of how cyber risks can impact operational continuity, stakeholder trust and long-term business value."
PwC’s 2027 Global Digital Trust Insights Survey found that 50 percent of respondents identify attacks targeting AI systems as among the cyber threats they are least prepared to address. However, just over one-fifth, or 22 percent, said they would authorise fully autonomous AI agents for cyber defence.
Based on the findings, PwC said cyber resilience will require director and senior management attention. It said less than half, or 47 percent, strongly agree cyber risk is a standing agenda item at Board level for their companies.
Nestle Maullon, risk assurance director at PwC Bahamas, said: "The organisations that will be best positioned for long-term success are not necessarily those investing the most in cyber security, but those making the most informed decisions.
“As AI adoption accelerates, leaders need visibility into the cyber risks that could most significantly affect their business and the confidence to align cyber security investments with their broader business objectives.
“When cyber security is embedded into strategy from the outset, it becomes more than protection. It becomes an enabler of innovation, resilience and sustainable growth."
PwC said its survey captured the views of almost 4,000 business and technology executives across 71 countries and territories. It added that companies are doubling down on their cyber investment amid rapid advances in AI, with the 84 percent of security and finance leaders expecting cyber budgets to increase up from 78 percent in 2025.
The accounting firm said that, as frontier AI models are rolled out, almost two-thirds (58 percent) of security leaders rank AI in their top cyber budget priorities for the upcoming year.
This comes as less than two-fifths (39 percent) of security, risk and operations leaders have a fully formalised and integrated operational continuity plan that specifically addresses cyber risks altogether.
When asked specifically about the cyber threats companies are least prepared to address, half of security leaders surveyed identify attacks targeting AI systems among their top threats, ahead of cloud-related threats (40 percent), third-party breaches (34 percent) and ransomware (33 percent).
PwC said that, even in the face of rising frontier AI vulnerabilities, companies have only implemented, on average, three out of seven key data risk measures. It added that only 5 percent of those surveyed have fully implemented every data risk measure - down from 7 percent last year.
While one-third, or 33 percent, of chief executives and security and risk leaders say their companies have established dedicated AI roles, including a chief AI officer or AI board, less than half strongly agree that cyber risk is a standing agenda item at the Board level (47 percent) or at executive leadership meetings (45 percent).
PwC added that, as cyber-attacks accelerate beyond human speed, AI is becoming an essential force multiplier for security teams. However, trust remains low – particularly around using autonomous AI agents.
This comes as attacks by autonomous botnets (53 percent), adversarial strikes (52 percent) and data poisoning (52 percent) rank among the top AI-enabled attacks that security and risk leaders say they are least prepared to address.
While security leaders rank threat detection and alerting (50 percent), and phishing detection and response (42 percent), among the top priority AI areas for cyber defence – roughly only one-fifth (22 percent) would authorise fully autonomous execution by AI agents for cyber defence,” PwC said of the survey findings.
It added thart rapid advances in AI, are proving problematic. More than half of respondents (55 percent) ranked reliability and maturity of AI technology among their top three barriers to increasing AI agent autonomy in security operations, while 46 percent cited accountability and explainability in AI decision-making.
In response, PwC said more than half (54 percent) of security and risk leaders are adopting multi-cloud or hybrid cloud strategies, while others are strengthening regional data and technology redundancy (47 percent) and localising infrastructure within specific jurisdictions (37 percent) to reduce concentration risk across their value chain.
As geopolitics shape the cyber risk landscape, PwC said half (50 percent) are also making changes to vendor, third-party and supply chain risk management.
As cyber budgets take centre stage, some companies are bringing in managed services to help, with AI the leading focus for 53 percent as companies confront a shortage of specialist cyber and AI talent.
To insulate their businesses against rapidly evolving AI and cyber threats, PwC said companies must strengthen cyber governance, accountability and risk decision-making; protect critical operations and build cyber resilience; secure data, AI and emerging technology; and manage ecosystem, third-party and technology concentration risk.
It also recommended that they use trusted technology and data to create enterprise value, and build their model to effectively leverage agents to defend against agent-enabled attacks.


Comments
Use the comment form below to begin a discussion about this content.
Sign in to comment
OpenID